Anomali: Iris Detect Feed
Overview
Section titled “Overview”DomainTools Iris Detect monitors internet infrastructure using the DomainTools discovery engine and domain data to detect and risk-score new domains within minutes. Available as a Premium Feed in the Anomali ThreatStream App Store, Iris Detect helps brand, fraud, and security teams respond quickly to emerging domain threats.
Prerequisites
Section titled “Prerequisites”Before you begin, ensure you have:
- ThreatStream access
- A valid DomainTools username and API key — see Authentication
- An active DomainTools Iris Detect subscription
- A DomainTools Monitor ID for your Iris Detect monitor (optional)
Activation
Section titled “Activation”Step 1: Navigate to the App Store
Section titled “Step 1: Navigate to the App Store”From the left navigation menu, go to App Store > App Store. In the search bar, type domain and press Enter. Locate DomainTools - Iris Detect in the results (listed as a Premium Feed).
Step 2: Open the feed details
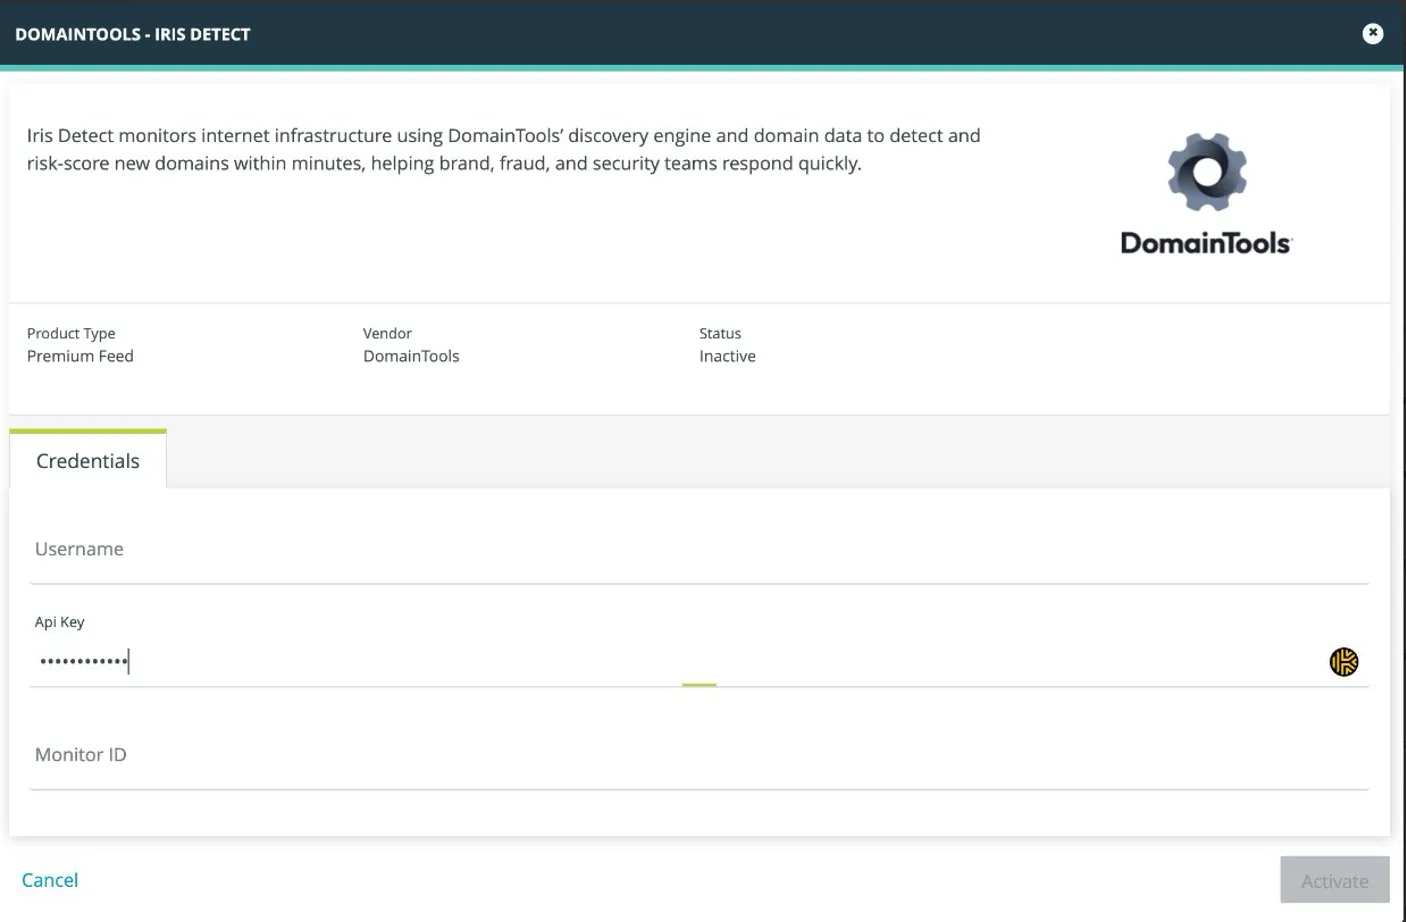
Section titled “Step 2: Open the feed details”Click the DomainTools - Iris Detect tile to open the product details modal. Confirm the following:
- Product Type is
Premium Feed - Vendor is
DomainTools - Status is
Inactive
Click I have credentials in the bottom-right of the modal.
Step 3: Enter your credentials and activate
Section titled “Step 3: Enter your credentials and activate”A Credentials tab appears with three fields:
- Enter your DomainTools Username.
- Paste your API Key.
- Enter your Monitor ID (optional).
Once all fields are complete, click Activate.
Finding your credentials
Section titled “Finding your credentials”- Username and API key: Available in your DomainTools account portal under API Credentials.
- Monitor ID: Found in the Iris Detect interface under your monitor settings. Each monitor has a unique ID.
Data mapping
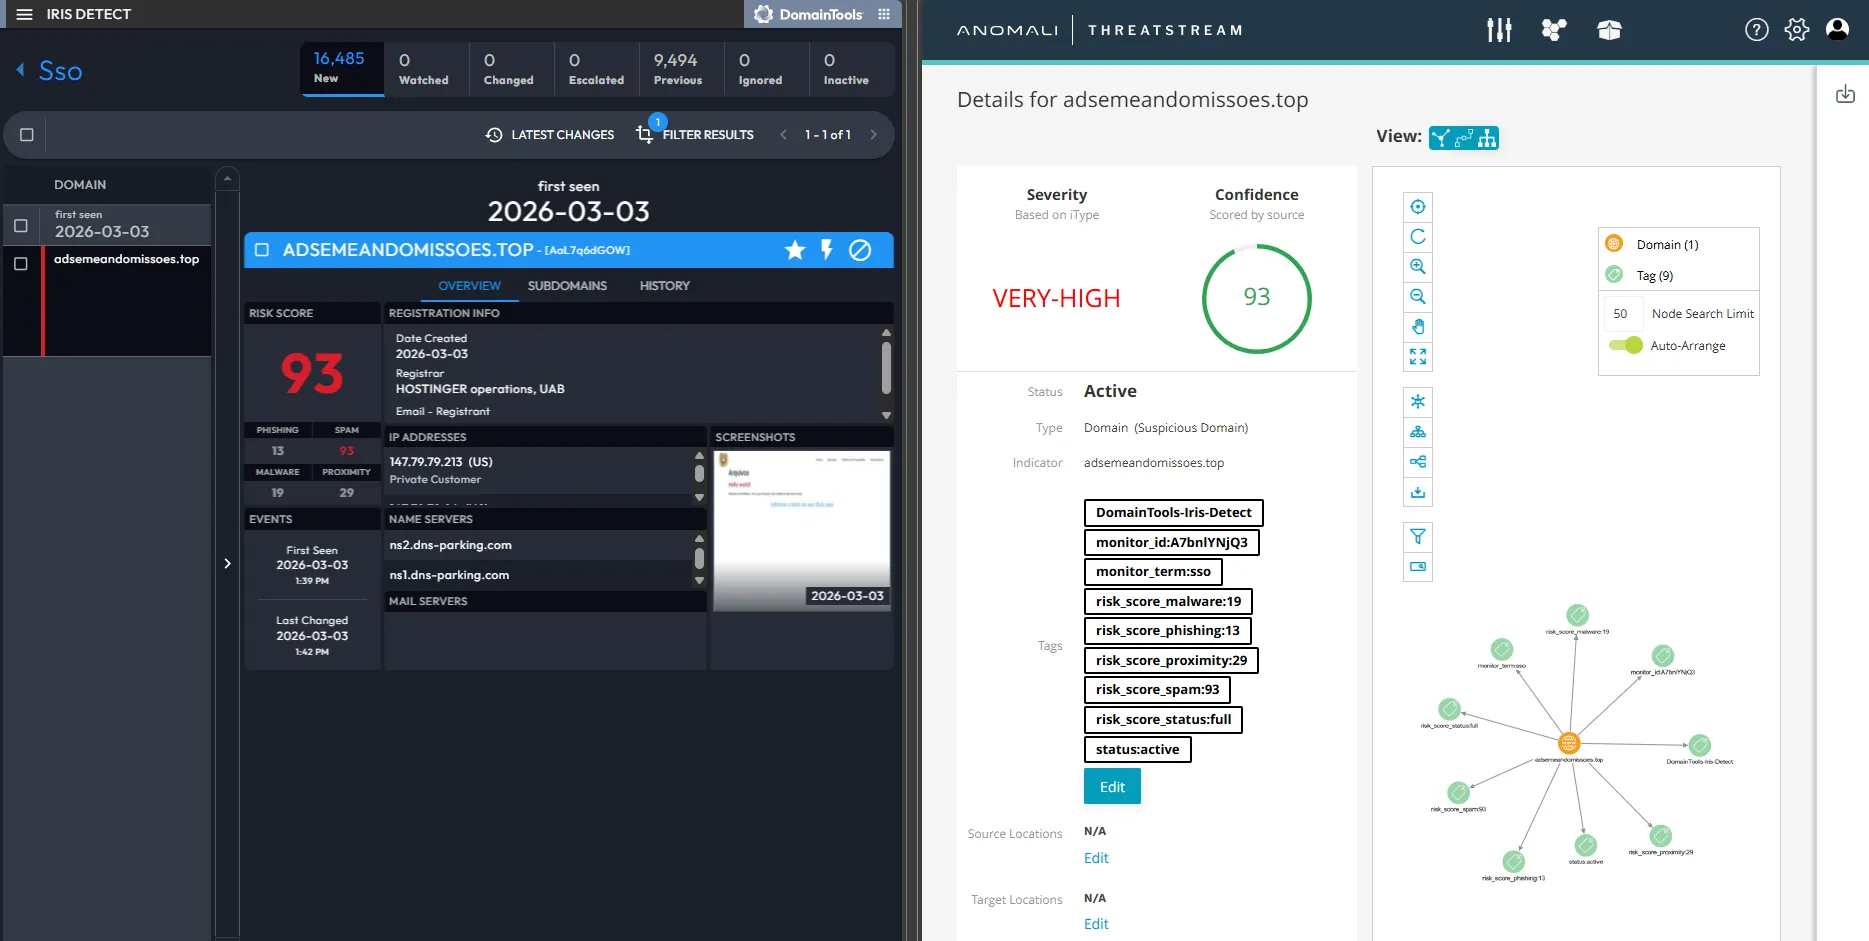
Section titled “Data mapping”The Iris Detect feed maps DomainTools domain data to Anomali ThreatStream fields:
| DomainTools Iris Detect | Anomali ThreatStream |
|---|---|
risk_score | Confidence |
discovered_date | Source Created |
changed_date | Source Modified |
| Risk score range | Severity (see mapping below) |
| Threat profile, Monitor ID, Monitor term, Domain status | Tags |
Severity mapping
Section titled “Severity mapping”Anomali severity is derived from the DomainTools Risk Score:
| Risk Score | Anomali Severity |
|---|---|
| 0 | low |
| 1–59 | medium |
| 60–89 | high |
| 90–100 | very-high |
| No score | medium |
Troubleshooting
Section titled “Troubleshooting”- Activate button remains grayed out: Ensure all credential fields (Username, API Key, Monitor ID) are populated before activating.
- Authentication error: Verify credentials are copied correctly with no leading or trailing spaces. Confirm your DomainTools subscription includes Iris Detect API access.
- Feed remains inactive after activation: Allow up to 15 minutes for the initial data sync. Check feed health in Manage > Feeds.
For additional support, contact your Anomali Customer Success Manager.